
.
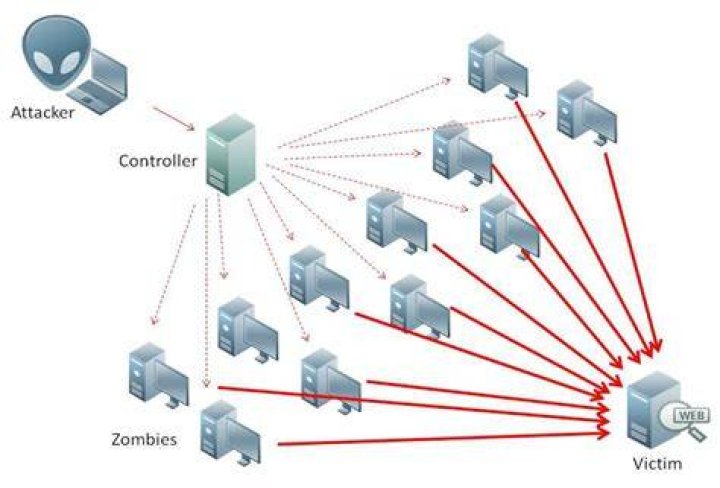
Similarly, it is asked, how does a DDoS attack work?
The DDoS attack will attempt to make an online service or website unavailable by flooding it with unwanted traffic from multiple computers. The attacker can then instruct and control the botnet, commanding it to flood a certain site with traffic: so much that its network ceases to work, taking the site offline.
Additionally, what are the types of DDoS attacks? Broadly speaking, DoS and DDoS attacks can be divided into three types:
- Volume Based Attacks. Includes UDP floods, ICMP floods, and other spoofed-packet floods.
- Protocol Attacks. Includes SYN floods, fragmented packet attacks, Ping of Death, Smurf DDoS and more.
- Application Layer Attacks.
Also to know is, what are DDoS attacks on WOW?
The DDoS attacks that hit World of Warcraft Classic started on September 7. In both the United States and Europe, DDoS attacks are charged as federal crimes that may lead to prison sentences of several years.
Is DDoS illegal?
DDoS attacks are illegal under the Computer Fraud and Abuse Act. Starting a DDoS attack against a network without permission is going to cost you up to 10 years in prison and up to a $500,000 fine.
Related Question Answers
Is DDoS a virus?
Distributed DoSA distributed denial-of-service (DDoS) is a large-scale DoS attack where the perpetrator uses more than one unique IP address or machines, often from thousands of hosts infected with malware.What is the biggest DDoS attack?
The biggest DDoS attack to date took place in February of 2018. This attack targeted GitHub, a popular online code management service used by millions of developers. At its peak, this attack saw incoming traffic at a rate of 1.3 terabytes per second (Tbps), sending packets at a rate of 126.9 million per second.How long do DDoS attacks last?
24 hours
Can you trace a DDoS attack?
People using a tool to conduct distributed denial-of-service (DDOS) attacks against other websites in support of WikiLeaks can easily be traced, according to computer security researchers.How do you identify a DDoS attack?
There are several clues that indicate an ongoing DDoS attack is happening:- An IP address makes x requests over y seconds.
- Your server responds with a 503 due to service outages.
- The TTL (time to live) on a ping request times out.
- If you use the same connection for internal software, employees notice slowness issues.
What is the best DDoS method?
Following are the methods of doing DDoS attacks:- UDP flood.
- ICMP (Ping) flood.
- SYN flood.
- Ping of Death.
- Slowloris.
- NTP Amplification.
- HTTP flood.
Can DDoS attacks steal information?
DDoS attacks cannot steal website visitors information. The sole purpose of a DDoS attack is to overload the website resources. However, DDoS attacks can be used as a way of extortion and blackmailing. For example, website owners can be asked to pay a ransom for attackers to stop a DDoS attack.What is DDoS in gaming?
DDoS attack - Distributed Denial of ServiceDDoS is short for Distributed Denial of Service. DDoS is a type of DOS attack where multiple compromised systems, which are often infected with a Trojan, are used to target a single system causing a Denial of Service (DoS) attack.Can firewall prevent DDoS?
Firewalls Can't Protect You from DDoS Attacks.Firewalls can't protect against complex DDoS attacks; actually, they act as DDoS entry points. Attacks pass right through open firewall ports that are intended to allow access for legitimate users.Can you DDoS a website?
If you want to DDos a website, put the web adress in the url box, if you have an ip you want to DDos then put the ip in the box. Then press the lock on button next to the text box you filled in.What port is DDoS?
port 80
What is an amplified attack?
An Amplification Attack is any attack where an attacker is able to use an amplification factor to multiply its power. Examples of amplification attacks include Smurf Attacks (ICMP amplification), Fraggle Attacks (UDP amplification), and DNS Amplification.What is Teardrop attack?
A teardrop attack is a denial-of-service (DoS) attack that involves sending fragmented packets to a target machine. Since the machine receiving such packets cannot reassemble them due to a bug in TCP/IP fragmentation reassembly, the packets overlap one another, crashing the target network device.What is DDoS attack in cyber security?
A distributed denial-of-service (DDoS) attack is an attack in which multiple compromised computer systems attack a target, such as a server, website or other network resource, and cause a denial of service for users of the targeted resource.How do you protect against DDoS?
7 Tips for Defending Your Network against DDoS Attacks- Document your DDoS resiliency plan.
- Recognize DDoS attack activity.
- Don't assume that only large-scale, volumetric attacks are the problem.
- Don't rely on traffic monitoring or thresholds.
- Don't rely on an IPS or firewall.
- Engage with a mitigation provider.
- Pair time-to-mitigation with successful attack protection.